Table of Contents
IP intelligence is the practice of enriching a raw IP address with context such as its geolocation, owning organization and ASN, connection type (residential, hosting, VPN, proxy or Tor), and reputation or threat history. Security, fraud and network teams use that context to decide how far to trust traffic coming from that address.
The bad news about lead generation is that, no matter how good your channels or strategies seem to be, some leads turn out to be low-quality, irrelevant to your goals, or downright fraudulent. Form fills with fake data, VPNs, scripts – all of that can burn your budget if you don’t have the right fraud prevention system in place.
Without traffic scoring, you might not even notice a rise in acquisition cost or buyer dissatisfaction. With IP intelligence tools, though, you can add an extra verification step before accepting or submitting the lead.
Read on to learn everything you need to know about IP intelligence for fraud detection.
What Fraud Does to a Sales Funnel
Lead generation fraud starts with a fake prospect that still triggers a payout. Bots and people with no real interest in the offer fill out the form, and the lead never produces a real conversion:
- Bots. Scripts fill out forms and send the data. Modern bots submit data at a slow pace, attempting to pass as real visitors. However, their traffic still often comes from data centers, cloud hosting, or Tor. IP intelligence tools examine whether the specific address belongs to one of those sources.
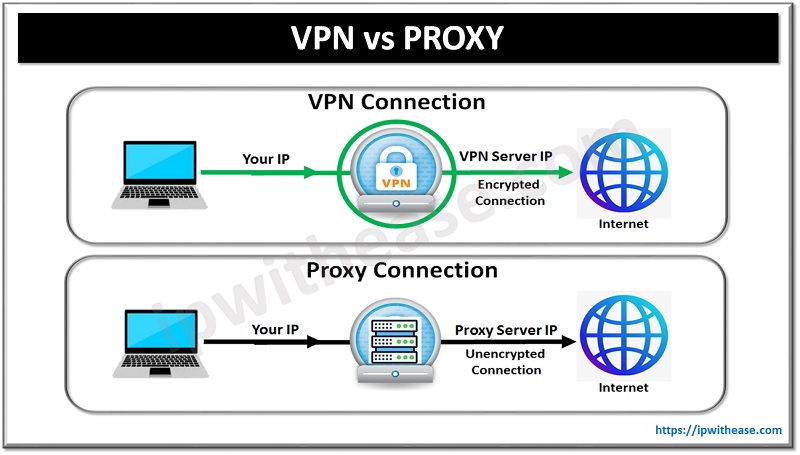
- VPNs and proxies. Fraudsters use them to pose as visitors from the offer’s target region. One person can then submit dozens of forms under different names, each from a different IP. Proxy detection checks those addresses against databases of known proxy networks. Advanced setups forge the IP in the HTTP headers (IP spoofing).
Yet sometimes fraud comes from real people. Incentivized traffic is the clearest case. They most likely won’t convert. These visitors connect from ordinary home networks, and IP intelligence returns a clean result.
Some fraudsters may even use stolen data. For you, it means leads that look like real people, but the person on the other end never filled out the form.
A visitor who submits a form twice on a slow connection sends two forms. The second copy is rejected as a duplicate. Locking the submit button after the first click prevents double-clicking, and comparing each new lead with recent ones by email or phone saves you from accidental duplicates.
How the IP Fraud Score Works
Fraud scoring starts with a set of independent tests, and each of them examines one aspect of the address:
- Hosting: Checks whether the address belongs to a data center or a cloud provider. Real consumers rarely browse from these networks, and the exceptions are privacy-conscious users who route their traffic through a cloud-hosted server.
- VPN, proxy, Tor: Shows whether the visitor is masking the real route. Tor alone proves nothing. Its addresses are hard to trace, and bots use them often.
- ISP and network type: Shows whether the visitor is masking the real route. Tor passes traffic through a chain of relays that hides the original address. Privacy-minded people rely on it, and bot operators do too.
- Geo mismatch: Compares the IP location with the ZIP code in the form.
- Reputation: Check the lead against blacklists and a history of suspicious activity.
- Device and OS: Helps catch forged or inconsistent device data, such as several different device signatures coming from one IP.
The tests feed one IP fraud score. A single mismatch can be accidental, and a VPN user or a vacationing visitor may well be a real prospect. IP intelligence platforms rate an address on the full set of tests.
Where to Place the Check and What to Do with the Score
IP intelligence can cut obvious data center traffic at page load, before the form even renders. A second pass at submit compares the ZIP code from the form with the IP location, with mismatches lowering the score.
Ask your developer to confirm that the check reads the visitor’s IP from your CDN, because a fraudster can fake the address the browser reports and get a clean score.
The score for that address maps to one of these actions:
- Allow. Clean traffic goes straight through.
- Pause. A user sees an additional check, such as a behavioral CAPTCHA.
- Flag. The lead goes through, and the score and the reason are recorded with it.
- Block. The form never loads for the visitor, or the lead never gets written to the CRM.
A synchronous IP intelligence check waits for the score before the lead moves on and can reject the lead on the spot. An asynchronous check scores in the background while the lead goes through right away. You can score every request. A check placed after email and phone validation only sees the leads that survived those steps.
Where to Draw the Line on the IP Score
SaaS fraud patterns usually show up as a combination of signals. So, always weigh multiple factors and use lead verification software. For example, you might want to block only the riskiest end of the score range at first, while checking reject and return rates to see how leads perform with advertisers. You can also examine conversion rates to see whether accepted leads turn into sales.
One thing to keep in mind, though, is that IP intelligence sometimes can rate a real visitor as risky. This happens to people on a VPN or on a shared hotel network, and these real visitors are false positives.
To lower false positives, add a honeypot field in the form. Most bots will fill it, so you can cut them off. Advanced bots or fraudsters that fill the form manually can pass it.
What to Check in Google Ads After the IP Score
The ad platform’s report lists every click with its country and time. Clicks from outside the target geo most likely won’t convert. Bursts of clicks seconds apart show up in the timestamps. Analytics records what happened after the click, and a session that ends within a second can come from a script.
To stay ahead of lead fraud threats, buy from vetted sources. Group your leads by source and compare their IP intelligence scores. If suspicious leads trace back to one source, pause it until you find the cause.
Google Ads accepts up to 500 excluded IP addresses per campaign, and a rotating proxy network cycles through a pool much larger than that. A fraudster is usually on a fresh address before the old one is listed. The exclusion list is best spent on addresses that keep returning in your landing page or tracker logs – everything else is left to IP intelligence.
ABOUT THE AUTHOR
IPwithease is aimed at sharing knowledge across varied domains like Network, Security, Virtualization, Software, Wireless, etc.